TL;DR

Get home office essentials delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
Ledger says all user reports of unexpected cryptocurrency withdrawals it investigated were linked to devices sold through Southeast Asian reseller CryptoBilis. The company confirmed an unauthorized hardware implant in at least one affected device, while researchers have described implants designed to capture wallet activity and send data over LTE. The number of affected users and the exact tampering method remain undisclosed.
Ledger has confirmed that at least one device tied to reports of drained cryptocurrency wallets contained an unauthorized hardware implant, and says all reports it investigated involved wallets sold through Southeast Asian reseller CryptoBilis. The company has not disclosed how many customers lost funds or exactly how the affected devices were altered.
Ledger began investigating after users reported losing cryptocurrency from wallets bought through CryptoBilis, a Malaysia-based retailer operating across Southeast Asia. On October 9, the company said it had opened an investigation and asked the reseller to stop selling and shipping Ledger devices. The next day, Ledger confirmed that one impacted user’s device had been tampered with.
In a subsequent update, Ledger said all user reports of unexpected fund drains it had received were associated with devices sold through CryptoBilis, describing the affected volume as “limited.” It has not provided a count of reports, confirmed losses, or affected devices. Ledger said it was contacting impacted users and working with authorities to identify the person responsible.
Security researchers and people examining devices have reported implants in Ledger Nano X wallets. Their findings are not the same as Ledger publicly confirming every technical detail: the company has confirmed an implant in at least one device, but has not identified the compromised model or disclosed a complete account of the mechanism. Researchers say examined versions included hidden circuitry and LTE connectivity that could transmit captured information.
Risks From Tampered Wallet Devices
The incident highlights a risk that differs from a software vulnerability: a device can be altered before it reaches its buyer, including through a reseller or other part of the distribution chain. Hardware wallets are designed to keep the private keys controlling crypto assets offline, but that protection depends on the device and its setup being trustworthy.
For customers, the practical concern is that a modified device may expose sensitive information despite appearing to be a genuine product. Ledger advises anyone who bought a device from CryptoBilis and has not set it up not to begin setup. Customers who already used one should consider moving assets to a new Ledger signer with a new seed, the company said. Anyone responding to the incident should rely on official Ledger guidance and avoid sharing recovery words with another person or website.
The case also raises questions for retailers and manufacturers about how returned or resold hardware is handled. Ledger says authorized resellers should source products through authorized channels and should not restock returned devices. The reported implant findings have prompted concern about the reliability of third-party sales, but the evidence provided so far does not establish that other resellers supplied compromised wallets.
hardware crypto wallet with LTE connectivity
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
How the Investigation Developed
Ledger devices store private keys and are used to authorize cryptocurrency transactions. The company offers a Genuine Check intended to verify a device’s authenticity. Ledger cautions that this check may not detect an added implant if the device’s original Secure Element—the component used for sensitive operations—remains intact. A successful authenticity check should not be treated as proof that no physical modification is present.
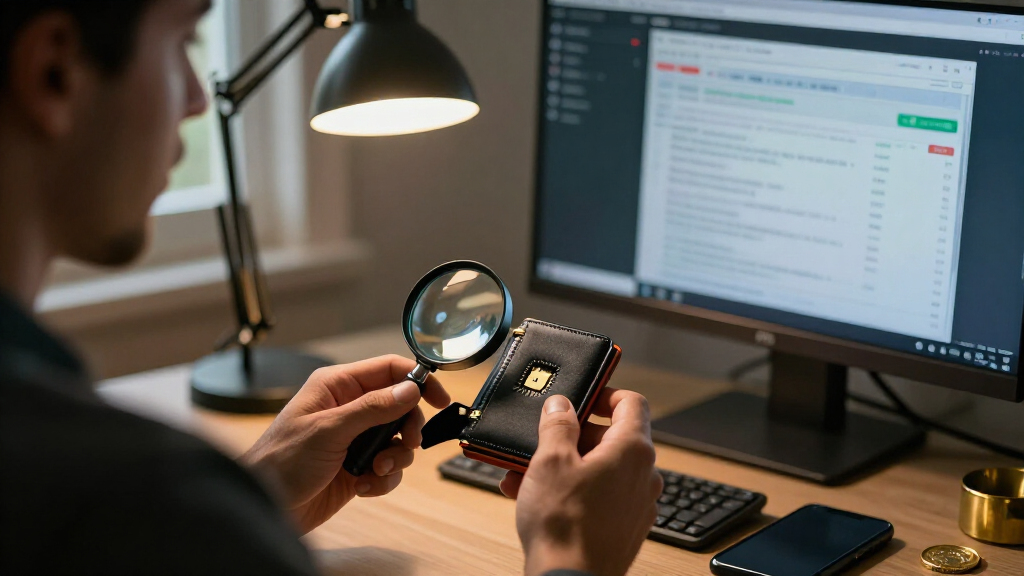
Researcher Mark Karpelès shared an image of an implant found in a Ledger Nano X and said it was concealed behind the screen. Tibane Labs later reported examining two variants in devices obtained through marketplaces in Japan, including one bought from a China-based seller and shipped from Malaysia. The researchers described a smaller replacement battery in one specimen and a second design fitted beneath the display. They reported finding a microcontroller, a small eSIM and an LTE module, and said antenna wiring was a visible clue in the devices they examined.
Those technical observations describe the samples examined by researchers, not necessarily every device involved in customer reports. Ledger has not publicly confirmed the models or components in all affected units. The company’s warning about unauthorized resellers reflects the risk of modified or counterfeit devices entering the supply chain, rather than confirmation that a wider set of retailers was involved.
““Ledger can confirm that one of the impacted users’ devices contained an unauthorized hardware implant.””
— Ledger
As an affiliate, we earn on qualifying purchases.
Scale and Tampering Method Remain Unknown
Ledger has not said how many users or devices were affected, the total value of reported losses, or when and where the tampering occurred. Its description of the volume as “limited” was not accompanied by figures. The company has confirmed an implant in one impacted device, while researchers have described two variants in samples they obtained; the connection between every examined sample and the customer reports has not been fully detailed publicly.
It is also unclear who altered the devices, how they entered the reseller’s inventory, and whether any other sales channels were involved. Ledger said there was no indication at the time of its report that other Ledger resellers were shipping compromised wallets. That statement does not establish that every device sold elsewhere is free of tampering.
As an affiliate, we earn on qualifying purchases.
Customer Warnings and Inquiry Continue
Ledger says it is contacting impacted users and working with authorities as its investigation continues. Customers who purchased through CryptoBilis should follow the company’s published instructions and contact Ledger through official support channels if they need help determining what to do. The company has asked the reseller to halt sales and shipments of its devices.
Further updates may clarify the number of affected devices, the scale of customer losses, and whether investigators can establish how the implant was installed and distributed. Ledger has also urged its authorized distributors to buy through approved channels and not put returned devices back into stock. No additional compromised resellers or a final investigation finding have been announced in the supplied reporting.
As an affiliate, we earn on qualifying purchases.
Key Questions
What has Ledger confirmed?
Ledger confirmed that at least one device belonging to an impacted user contained an unauthorized hardware implant. It also said the user reports of unexpected fund drains it investigated were linked to devices sold through CryptoBilis.
Which wallets or sales channel are linked to the reports?
Ledger linked the reports to devices sold by CryptoBilis, a Malaysia-based reseller. Researchers have described implants in Ledger Nano X samples, but Ledger has not publicly confirmed that every affected device was that model.
What should CryptoBilis customers do?
Ledger advises customers who have not set up a device bought from CryptoBilis not to start setup. For a device already set up, it says users should consider moving assets to a new Ledger signer with a new seed. Customers should consult Ledger’s official guidance for instructions.
Can Ledger’s Genuine Check detect an implant?
Not necessarily. Ledger says its Genuine Check may not detect an added implant when the device’s original Secure Element remains intact, so a successful check does not rule out every form of physical modification.
How many people or devices were affected?
Ledger has not disclosed a number. The company described the affected volume as “limited,” but has not published a count of devices, users, or the value of reported losses.
Source: hn
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.